R1 CriticalMET
Private unified command center
Authorized members can navigate every operating surface. Fresh unauthenticated access fails closed without client data or auth cookies.
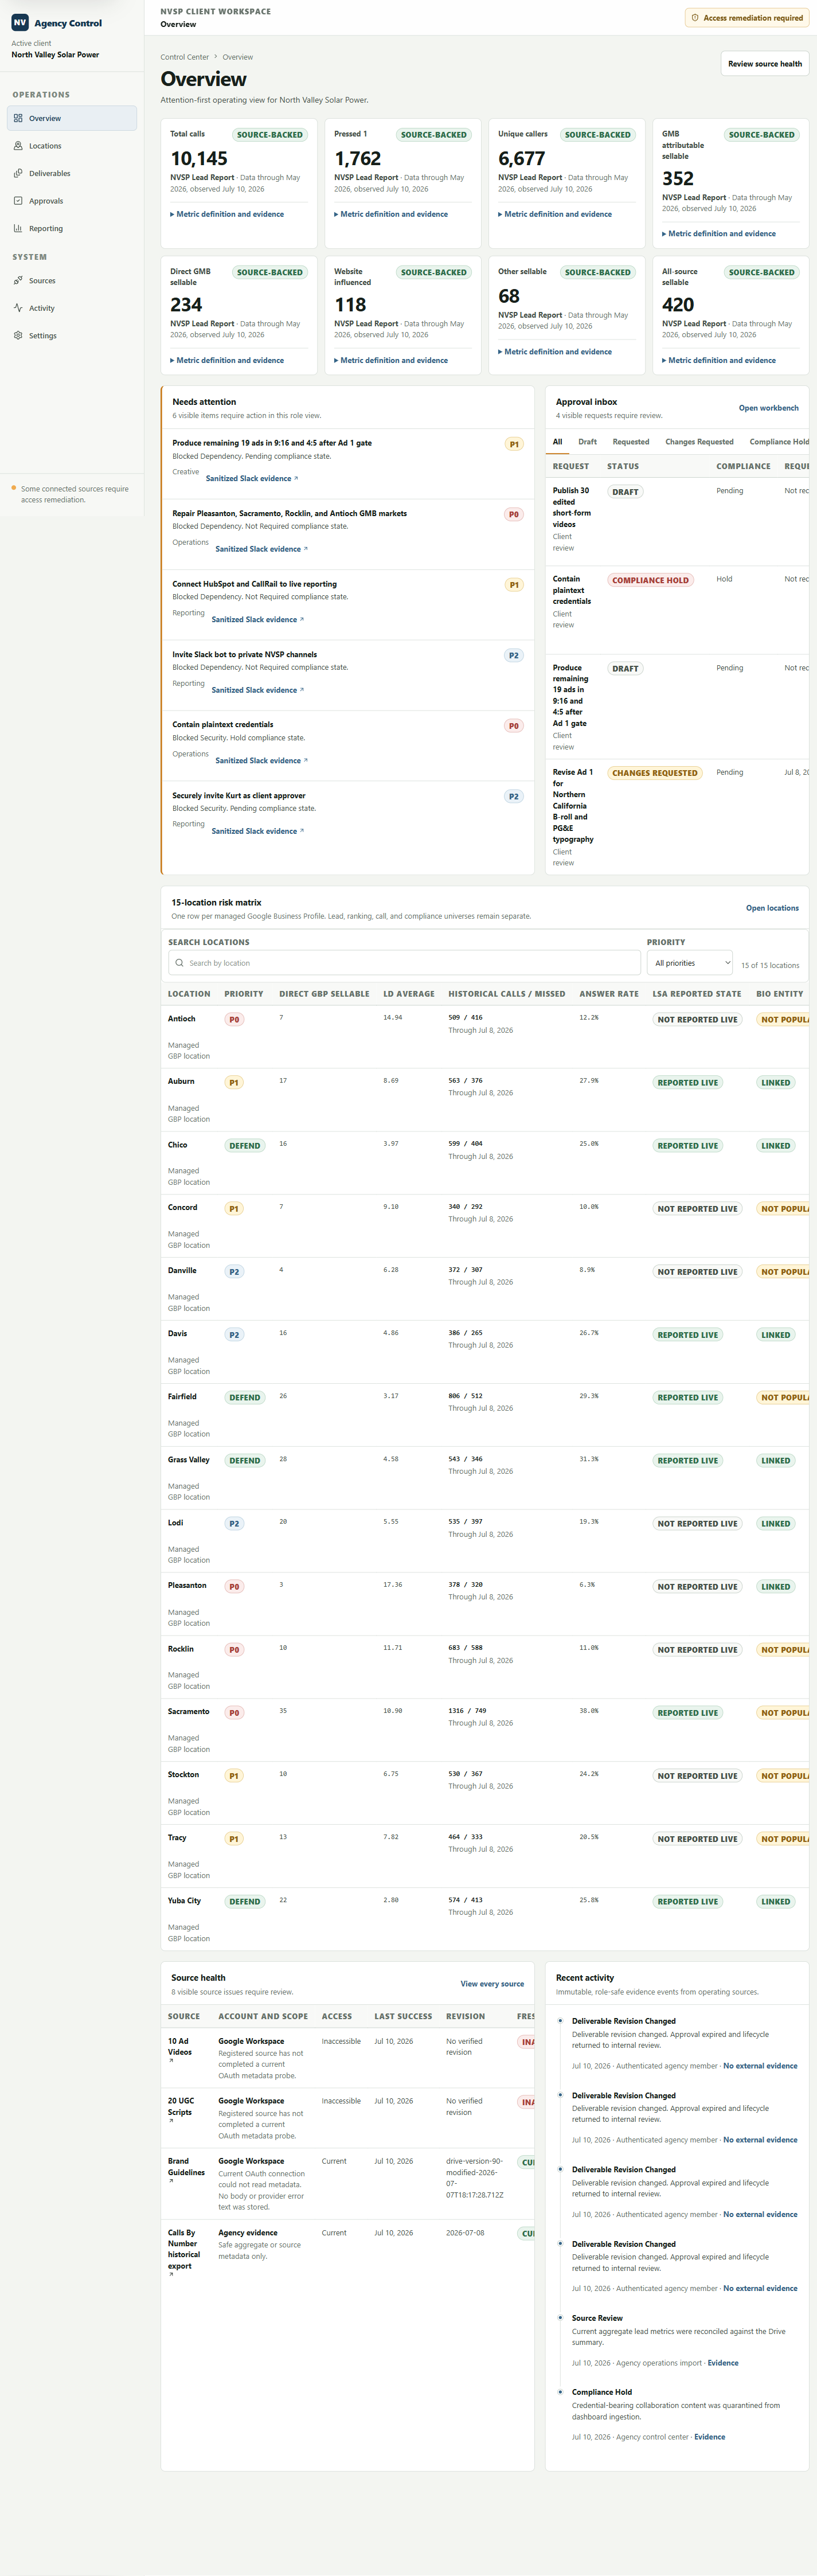
Master client summary and Proof of Work Done
Reporting, all 15 locations, 23 deliverables, revision-safe approvals, Google source health, Slack operating state, and immutable activity are now organized in one protected production workspace.
Counts come from the production read model and the final validated release.
Every line was formed before final observation, checked on the deployed URL, and approved by a second verifier.
Authorized members can navigate every operating surface. Fresh unauthenticated access fails closed without client data or auth cookies.
KPIs, attention, approvals, sources, and work remain explicit about current, stale, unknown, conflicted, inaccessible, and blocked states.
Aggregate metrics retain source, period, observation date, definition, universe, and evidence. Lead, historical-call, GSC, and local-rank universes stay separate.
All 15 locations expose role-safe facts, evidence, source-separated performance, incomplete state, and unresolved conflicts.
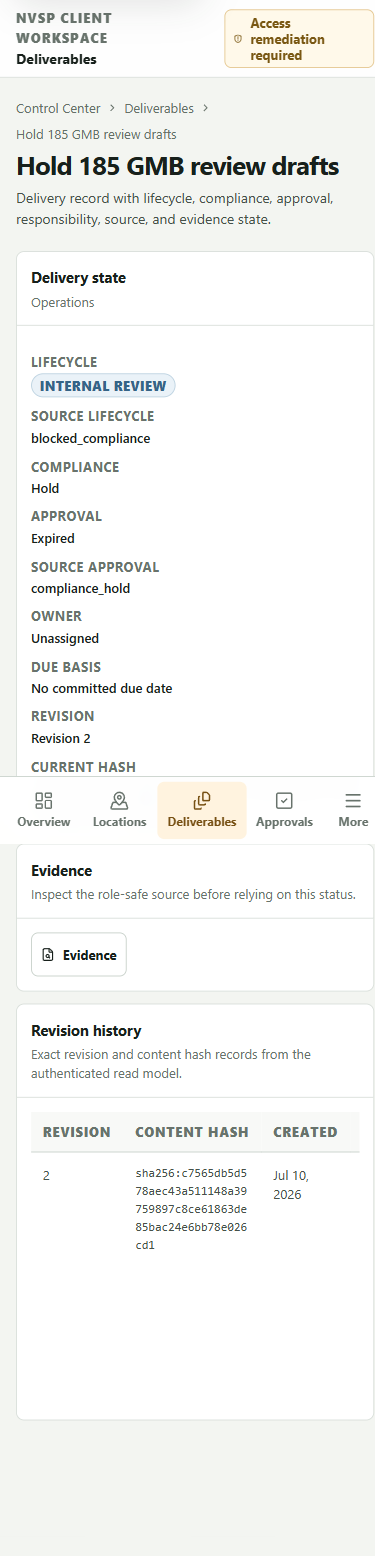
All 23 work items include lifecycle, compliance, approval, owner, due basis, source, revision, and exact revision history.
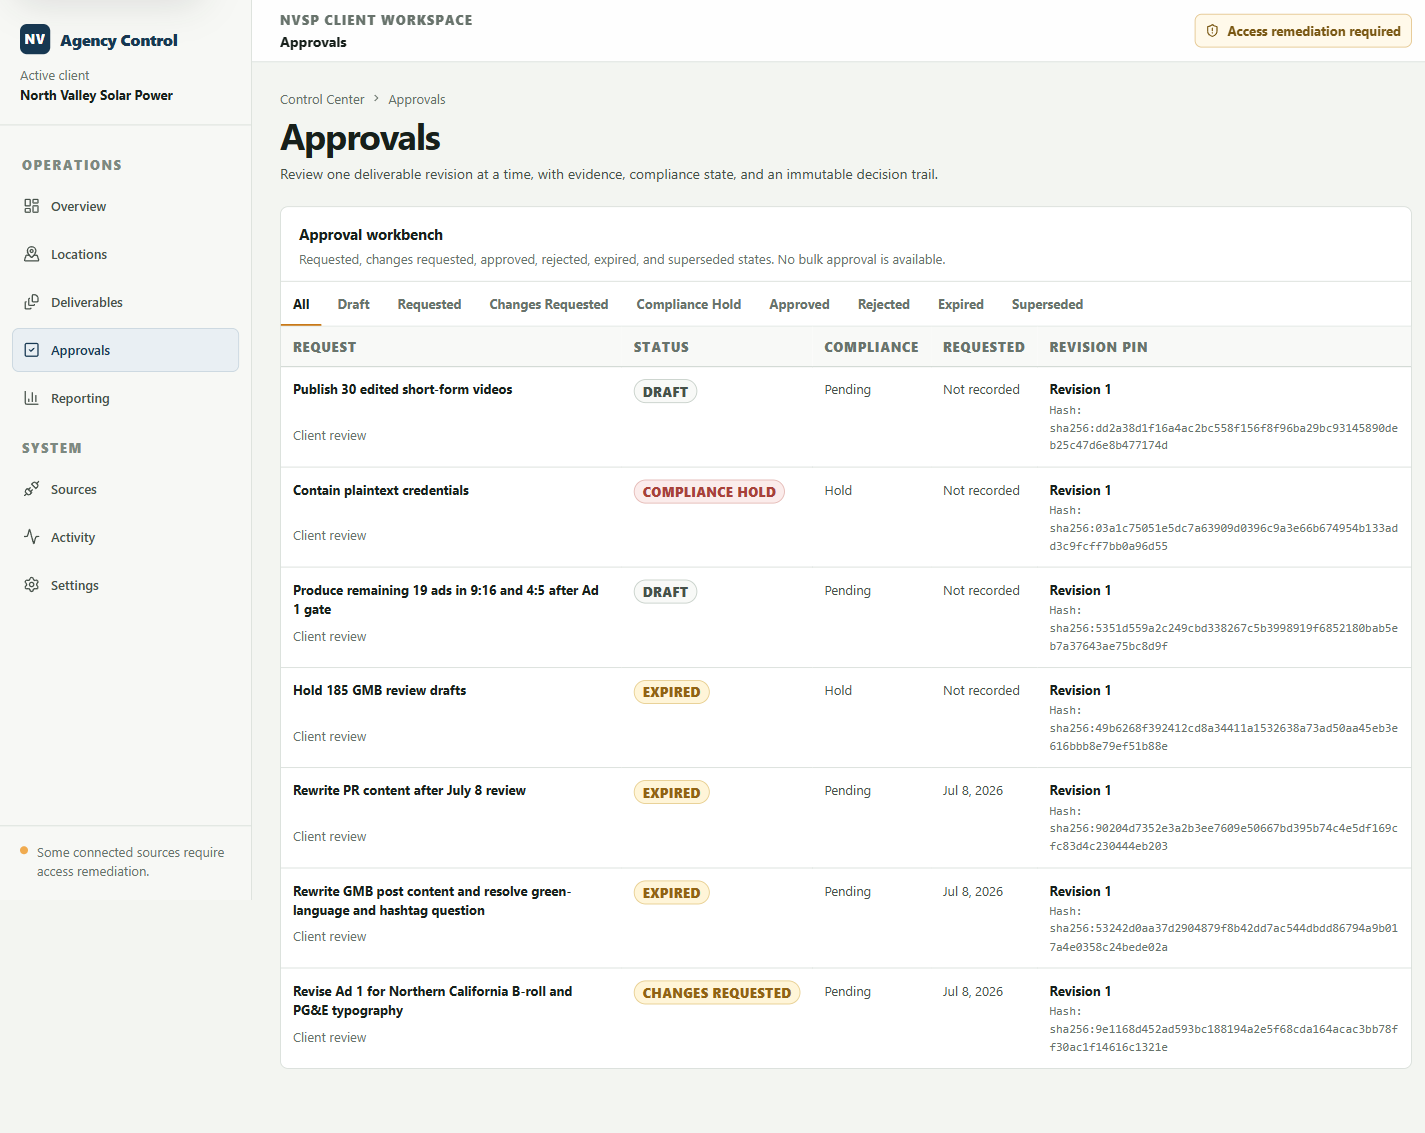
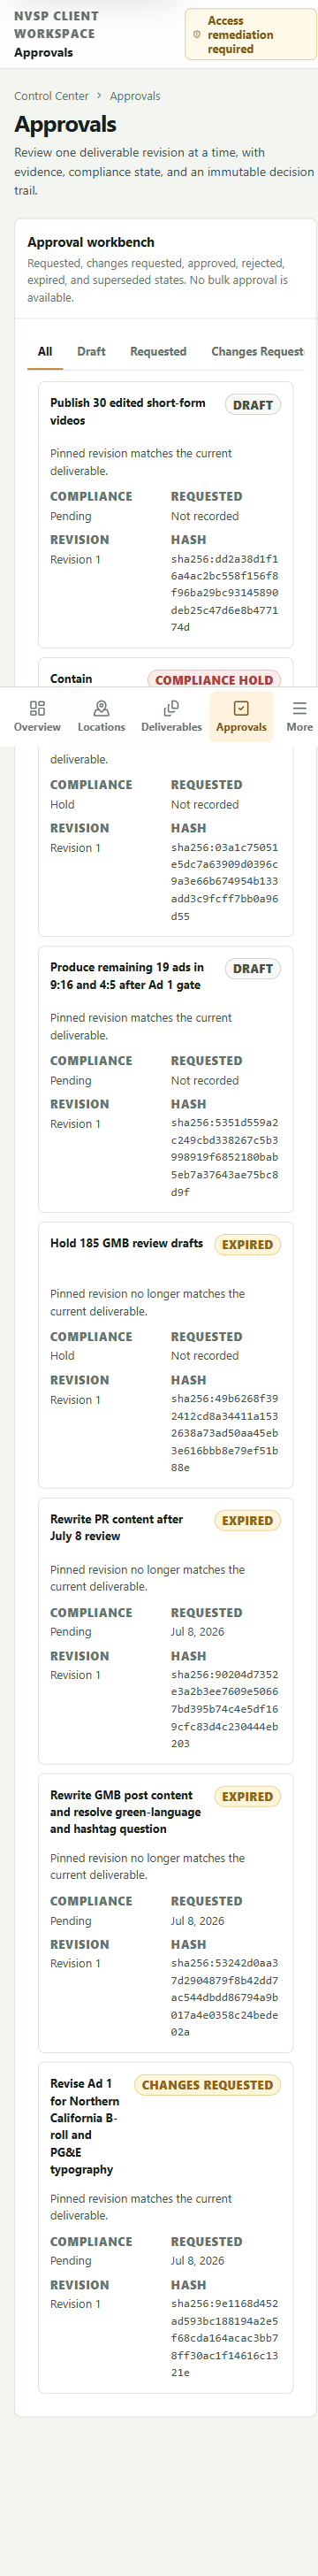
All 7 requests are role-gated and revision-bound. Holds, stale versions, and hash conflicts prevent unsafe decisions, and no bulk approval exists.
All 27 sources remain visible, including 21 Google sources and 2 Slack channels, with truthful current, stale, inaccessible, and blocked health.
Admin-only allowlisted metadata sync records an idempotent per-source ledger and safe errors without retrieving file bodies or spreadsheet rows.
Both private channels use safe IDs and links. Notifications remain visibly blocked and retryable until the bot is invited, with no raw messages stored.
Immutable events cover revision expiry, approval state, source review, sync, compliance, and notification state.
Vercel SSO, Supabase authentication, membership, four roles, client-safe projections, and forced RLS deny unauthorized and cross-client access.
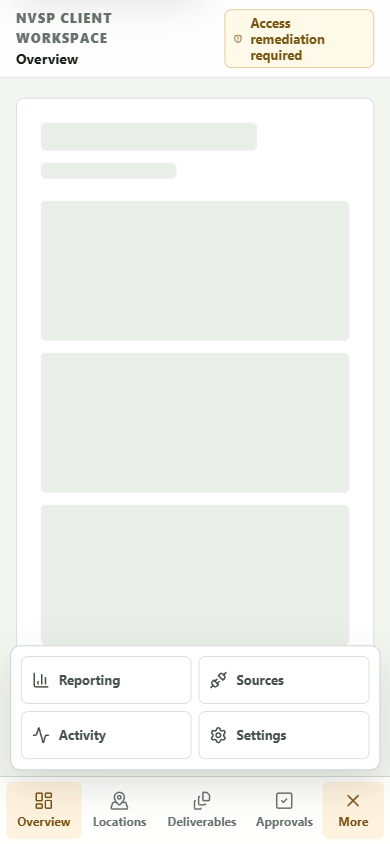
Every mobile route is width-contained, axe-clean, keyboard reachable, and free of console, warning, and application HTTP errors.
Failures stay visible. Nothing is silently omitted or presented as complete when access is missing.
| Measure | Result |
|---|---|
| Processed | 21 |
| Accessible | 16 |
| Inaccessible | 5 |
| Redacted | 0 |
| Quarantined | 0 |
| Run outcomes | 15 succeeded, 1 partial, 5 failed |
No retry was performed. The preserved ledger is the evidence source.
drive_http_404drive_http_404drive_http_404drive_http_404drive_http_404sheets_http_404Main private channel: C0B4FN3SBTJ
Video channel: C0BCXVDV54J
Outbound approval notifications are blocked and retryable because the bot is not yet invited to the private channels. The dashboard states this openly.
The private workspace uses layered deployment, session, membership, role, projection, and database controls.
Shared infrastructure note: the Master Brain project separately contains 32 unrelated public tables with RLS disabled. Those tables were not changed here. See the official Supabase RLS guide.
The final release closed every issue found by the independent verification chain.
Every thumbnail opens the full production capture. The primary set is from exact final commit 770aa11.


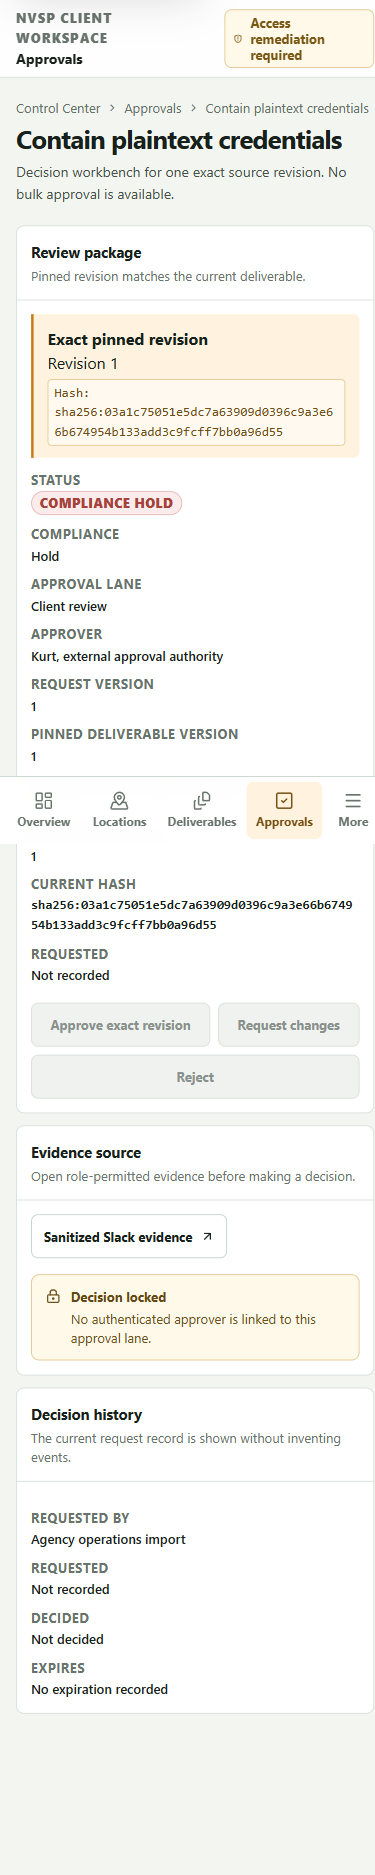


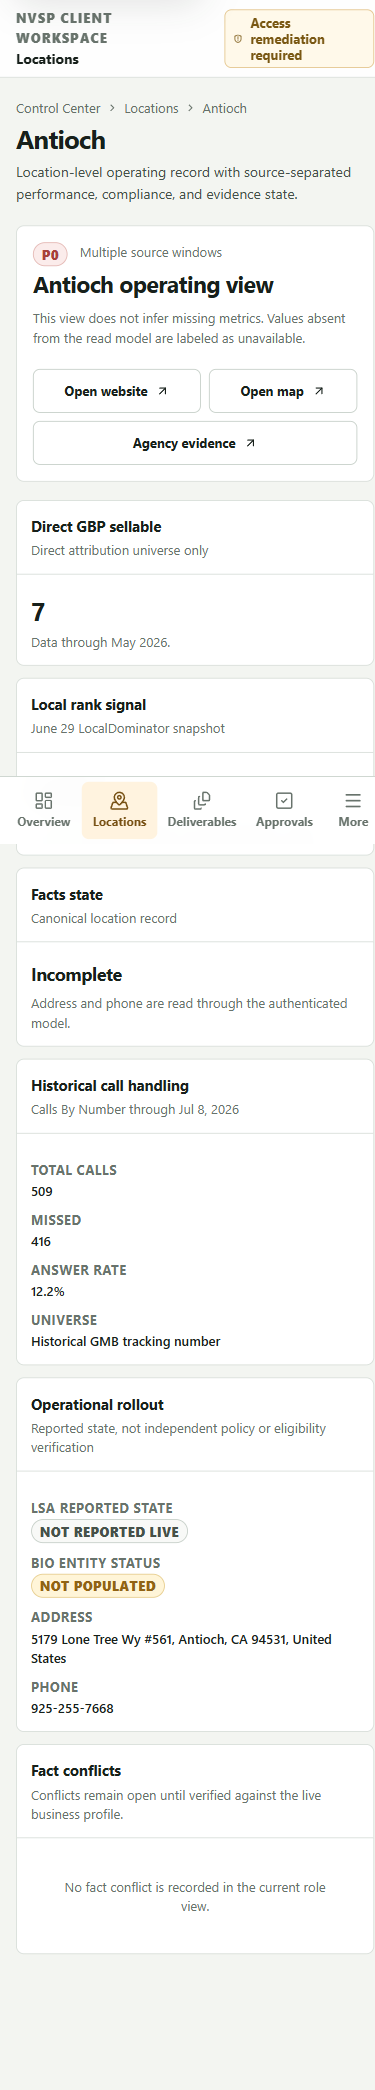

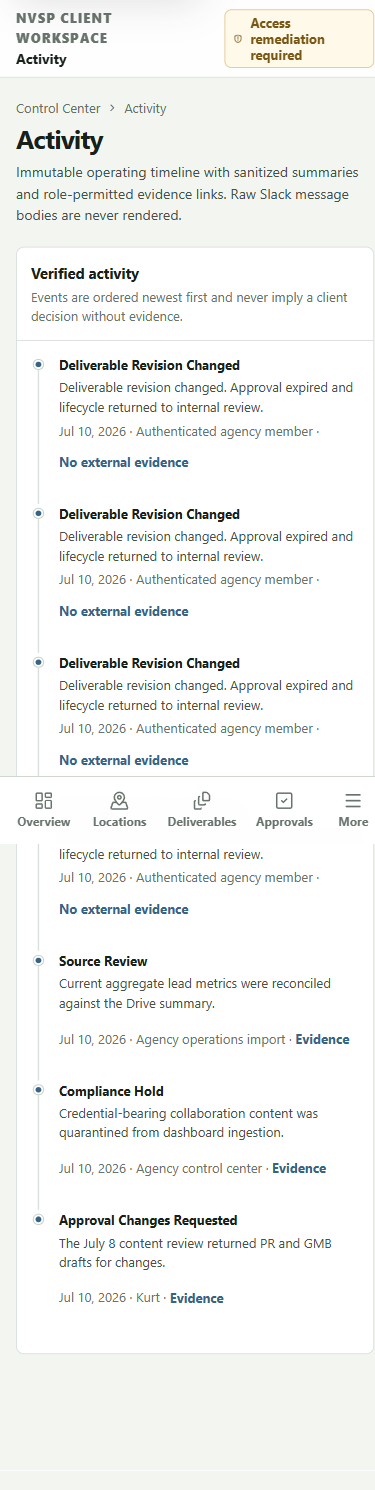
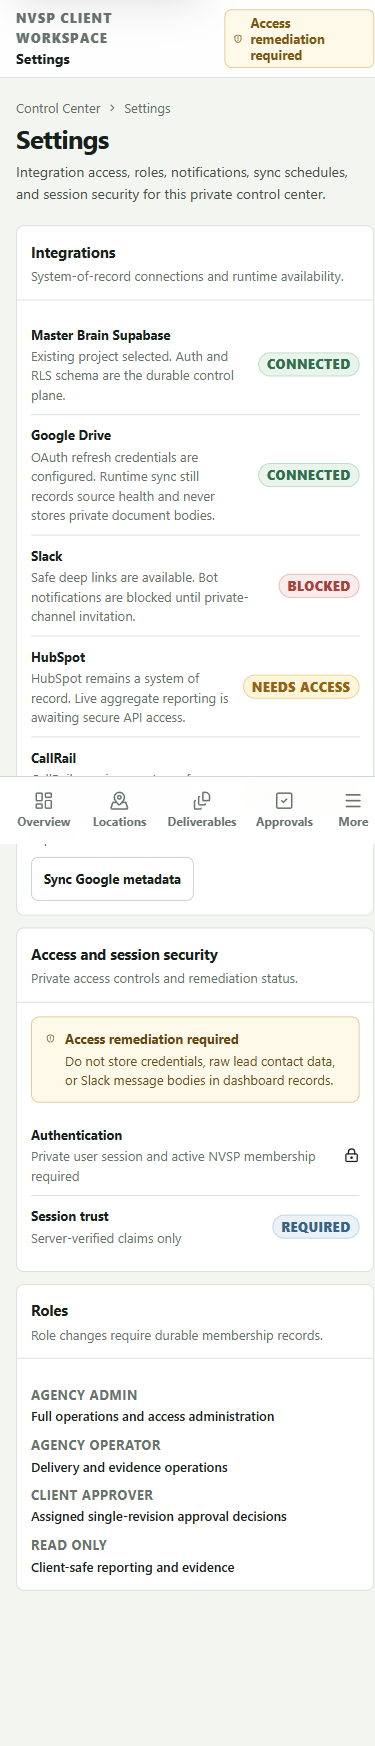
The application is shipped. These dependencies remain accurately represented so the team knows what requires outside access.
Invite the notification bot to both private channels before enabling outbound approval delivery. Until then, delivery stays blocked and retryable.
Resolve ownership or link access for the five missing Drive sources and the partial Weekly Facebook Ads Report. Their failure state remains visible in Sources and Settings.
Queen verified the deployed release. Carlos independently reverified all 12 requirements. The deterministic gate passed.
